เวิร์กโฟลว์ asset เกม AI
Updated 2026-09-05
กำหนด asset ที่เกมต้องใช้ เก็บที่มาและ permissions แล้วตรวจผลที่ import ในขนาดการเล่นจริงก่อนใส่ใน release
เขียน asset contract ก่อนสร้าง art
กำหนดหน้าที่ของ asset ในเกม: player sprite, obstacle, background tile, button, sound cue หรือ promotional material ระบุ dimensions, transparency, frame layout, viewpoint, palette constraints และ scale ที่จะตรวจ ถือสิ่งเหล่านี้เป็น production inputs ไม่ใช่หวังว่าภาพที่สวยจะพอดีในภายหลัง
สำหรับ sprite sheet ให้กำหนด frame count, cell dimensions, origin และ animation states ที่คาดหวัง สำหรับ UI asset ให้ระบุข้อความรอบข้างและ interaction state ใช้ placeholder ที่เป็นของคุณจน contract เสถียร เพื่อไม่ให้ art iteration บังคำถามว่า gameplay ทำงานหรือไม่
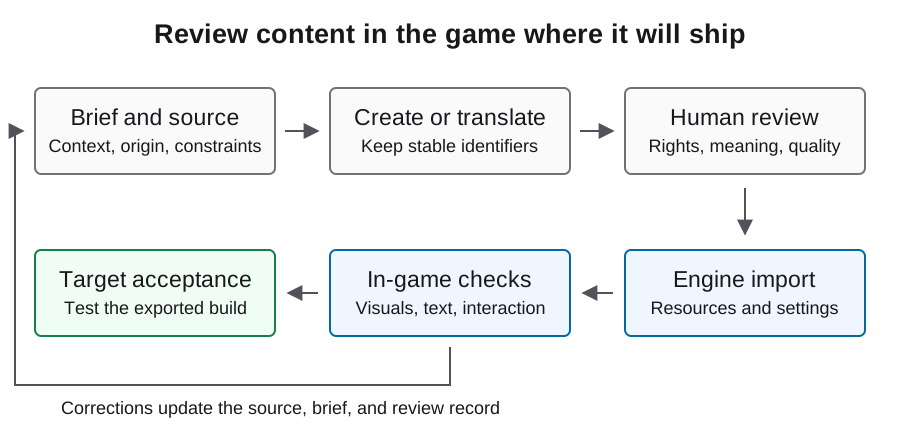
เลือก source ที่มี permission basis ให้รีวิวได้
source ที่เป็นไปได้มีงานที่ว่าจ้างต้นฉบับ asset ที่สร้างเอง licensed pack หรือ material ที่สร้างภายใต้ service terms ที่รีวิวแล้ว เปรียบเทียบจาก permissions, editability, consistency และ review effort ไม่ใช่ claim ที่ไม่มีหลักฐานว่า source ใดถูกกว่าเสมอ
เก็บ source link เดิมและ license หรือ agreement ที่ใช้กับ asset record บันทึก attribution และ redistribution requirements material ที่สร้างขึ้นก็ต้องรีวิว input และ output การเข้าถึงโมเดลไม่ได้ยืนยัน clearance ของตัวละคร เครื่องหมาย หรือ material ที่ได้รับการคุ้มครอง หากสิทธิ์ไม่ชัดให้ยกระดับก่อนแจกจ่าย อย่าเปลี่ยนความไม่แน่นอนให้เป็น approved status
| เส้นทาง source | หลักฐานที่ต้องเก็บ | Technical review |
|---|---|---|
| งานต้นฉบับ | บันทึกผู้สร้างและ ownership | Export settings และ edit source |
| Licensed pack | License, source และ attribution duties | Scale และ import compatibility |
| Generated material | Tool identity, input rights และ terms review | Consistency, cleanup และ frame usability |
แยก coding และ image production ให้ระบุที่มาได้
Astra อาจเป็นหัวข้อของ coding experiment ขณะที่ image tool อื่นสร้าง art บันทึกบทบาทเหล่านั้นแยกกัน คำสั่งข้อความที่ขอ sprite ไม่ได้พิสูจน์ว่าบริการใดสร้าง pixel และ code session ที่สำเร็จไม่ได้ให้ image-service bill
สำหรับ output ที่สร้างแต่ละรายการ เก็บ image tool identity จริง request record หากมี generation settings output ที่เลือก และ manual edits ใส่ความพยายามที่ fail หรือทิ้งใน usage ledger ติดตาม image work แยกจาก text coding แม้เอเจนต์เดียวจะ orchestrate ทั้งสอง เพื่ออธิบายได้ว่าต้นทุนและแรงงานคนเกิดตรงไหน
ใช้ manifest ที่แสดง unknown อย่างซื่อสัตย์
ใช้ record ตัวอย่างด้านล่างกับ asset pipeline และคงฟิลด์ที่ยังไม่ตรวจเป็น null จนกว่าจะ review การอนุมัติต้องมี source จริง permission decision file identity และ technical review คง asset identifier เดิมเมื่อแทนที่ output เพื่อให้ไฟล์ใหม่รับ context ได้โดยไม่รับ approval ที่ยังไม่ earned
เชื่อม raw material กับ final imported output ด้วย asset identifier เดียวกัน เมื่อคนลบพื้นหลังซ่อม animation frame หรือเปลี่ยน contrast ให้บันทึก transformation สิ่งนี้ทำให้ replacement, attribution review และ debugging ภายหลังทำได้โดยไม่ต้องพึ่งความจำจาก chat session
{
  "asset_id": "player_idle",
  "source_url": null,
  "permission_record": null,
  "creator_or_tool": null,
  "source_hash": null,
  "final_file_hash": null,
  "transformations": [],
  "image_cost_record": null,
  "review_status": "pending",
  "import_result": null
}
ตรวจ engine import ไม่ใช่แค่ source file
เอกสาร image-import ของ Godot อธิบายตัวเลือก compression และ mipmap ที่มีผลต่อ imported textures เลือก settings ตามเงื่อนไขการแสดงจริงของ asset pixel art, scaled backgrounds และ 3D textures ไม่ได้ใช้ preset สากลเดียว เก็บ settings ที่ใช้กับ output ที่อนุมัติ
ตรวจ transparent edges, background ที่ไม่ตั้งใจ, frame spacing และ visual scale ในเกม เปรียบเทียบ collision representation กับ object ที่มองเห็น PNG ที่ technically valid ยังใช้ไม่ได้หาก frame ทำให้ตำแหน่งที่เห็นของตัวละครขยับ หรือ sprite กลืนกับ level ปฏิเสธปัญหาเหล่านี้ก่อนกระจาย asset ไปหลาย scene
รีวิว animation, sound และ UI ในบริบทจริง
เล่น action ที่เกี่ยวข้องซ้ำและตรวจ transition ระหว่าง animation states ตรวจว่า timing ทางภาพตรงกับ collision และ feedback contact sheet แบบ frame-by-frame ช่วยตรวจได้ แต่ไม่แทนการดู animation ที่กำลังรันและ input ของผู้เล่นที่เรียกมัน
สำหรับ audio ให้ตรวจ level consistency, looping, timing และ permission records แยกจาก image checks สำหรับ UI artwork ให้ตรวจ focus, disabled states และ text contrast ที่ resolution เป้าหมาย บันทึก failure ตาม asset และ behavior เพื่อให้เอเจนต์ได้ feedback ที่นำไปทำต่อได้ ไม่ใช่คำขอกว้างๆ ให้เกมดูดีขึ้น
ตรวจ exported artifact และ disclosure inventory
ยืนยันว่า resource ที่รับรองแล้วอยู่ใน exported build และทำงานตามที่รีวิว เก็บ screenshot หรือ recording จาก artifact จริงเมื่ออ้าง implementation อย่าใช้ concept image หรือ generated mockup แทน gameplay evidence
รักษา shipping inventory ที่แยก artwork, sound, narrative, localization และ runtime output ใช้ Steam preparation guide และ Content Survey ปัจจุบันตัดสินใจว่าต้องอธิบายอะไรสำหรับเกมจริง asset record ภายในที่เสร็จช่วย review แต่ไม่ได้ยืนยัน platform approval หรือแก้คำถามสิทธิ์ที่ยังไม่ชัด
ตั้งงบสำหรับ asset ที่ยอมรับแล้วรวม rework
วัดการผลิต asset จากผลในเกมที่ยอมรับ ไม่ใช่แค่จำนวนไฟล์ที่สร้าง เก็บ rejected generations, manual cleanup, import corrections และ target-build rechecks ใน record ใช้ billing categories และวันที่ของ provider จริงแทนการฝังราคาในคู่มือ
เมื่อ generation ซ้ำๆ fail requirement ทางเทคนิคเดิม ให้ทบทวน asset contract หรือใช้ original placeholder ระหว่างแก้ gameplay พรอมป์เพิ่มไม่ชดเชย frame layout ที่ไม่กำหนด ขั้นตอนและ manifest fields เหล่านี้เป็นตัวอย่าง ประเมินไฟล์จริงและ terms ที่ใช้ก่อนถือ asset ว่า accepted หรือประเมิน production batch ถัดไป
คำถามที่พบบ่อย
Astra coding usage รวมต้นทุน art ทั้งหมดของเกมหรือไม่?
ไม่ ระบุ image และ audio services แยกกัน แม้เอเจนต์จะเรียกใช้ใน task เดียว ใช้ request และ billing records จริง
ใช้ภาพใดก็ได้ที่ดูเหมาะหรือไม่?
ตรวจ permission basis และ technical fit รูปลักษณ์เพียงอย่างเดียวไม่ได้ยืนยัน distribution rights หรือ animation และ import behavior ที่ใช้ได้
PNG โปร่งใสเป็น sprite ที่เสร็จแล้วหรือไม่?
ยังต้องตรวจ scale, origin, frames, edges, collision fit และ visibility ในเกมที่ตั้งใจ
asset manifest ควรมีอะไร?
Origin, permission record, creator หรือ tool identity, hashes, transformations, review state และ import evidence ข้อมูลที่หายควรคงเป็น unknown อย่างชัดเจน
ควรทำเครื่องหมาย asset ว่า accepted เมื่อใด?
หลัง permission record แก้ไขแล้ว imported file ตรง technical brief และ behavior ที่เกี่ยวข้องผ่านการตรวจใน target build